Cybersecurity · Responsible AI · Business mission

Secure the systems.Govern the AI.Advance your mission.

We equip your cybersecurity program with the engineering, compliance and risk capability to meet your security and compliance obligations. We help you manage AI responsibly through AI governance, risk and compliance, AI cybersecurity and AI solutions. Everything we do serves one purpose: helping you achieve your strategic business goals.

  1. Cybersecurity
  2. Responsible AI
  3. Business mission
SAM.gov
Active
UEI
UEQDZSKKRFGC65
CAGE
9DE87
Size
Small business
Primary NAICS
611430
Payment
Government purchase card accepted (up to the micro-purchase threshold), or invoice/purchase order for larger engagements
Capability statement (PDF)

Who we have worked with

Organizations we have trained, advised and supported

Federal agencies, defense organizations and contractors, state and local government, universities, financial services, healthcare and technology. The same practical, evidence-based approach, adapted to each mission.

  • 20organizations
  • Training
  • Consulting services
  • Prime contracts
  • Subcontracts
Government, defense and education
  • U.S. Department of Defense
  • United States Navy
  • Defense Information Systems Agency (DISA)
  • Cybersecurity and Infrastructure Security Agency (CISA)
  • U.S. Securities and Exchange Commission
  • Pension Benefit Guaranty Corporation (PBGC)
  • City of Baltimore
  • Washington Suburban Sanitary Commission
  • Bowie State University
  • Northrop Grumman
  • Signature Renovations
  • Arcal Precision Components
Financial services, healthcare and industry
  • Verizon
  • Citi
  • OceanFirst Bank
  • Aflac
  • MedStar Health
  • Chesapeake Employers Insurance
  • ISACA
  • ITDC

Logos identify organizations whose staff attended True CyberChampion or Dr. Beza training, or that received our services directly, under a prime contract or under a subcontract. They are trademarks of their respective owners, and their display does not imply endorsement.

Sectors we serve

  • Federal agenciesFISMA, RMF and compliance support for mission-critical systems
  • Defense contractorsCMMC readiness and controlled unclassified information protection
  • State and local governmentAI governance training, policy rollout and workforce readiness
  • Big techAI governance, algorithmic auditing and responsible AI deployment
  • HealthcareHIPAA compliance, health data security and AI governance
  • Financial institutionsFinancial services compliance, risk management and secure AI
  • Critical infrastructureSecurity and compliance for energy and utilities
  • Private sector and SMBsScalable cybersecurity, compliance strategy and AI readiness

We bring AI governance, engineering, and workforce skills together

True CyberChampion is a Washington, DC-area artificial intelligence and cybersecurity advisory, engineering, and training firm. We help government agencies, defense contractors, businesses, and regulated organizations adopt AI responsibly, build practical solutions, and develop the workforce skills needed to succeed.

We combine scientific research, hands-on engineering, cybersecurity and regulatory expertise, executive advisory, and adult education to help organizations move from policy and strategy to implementation and everyday practice.

We are scientists, engineers, researchers, and educators who understand that technology alone does not solve business problems. Organizations need sound governance, solutions that work, and people who know how to use them. Our approach is practical, customized, and focused on results.

  • AI governanceClear rules, managed risk, confident adoption
  • AI engineeringWorking solutions to defined problems
  • AI skills developmentPeople who can use AI well and safely

Delivery leadership

  • GWU and MIT alumni
  • Industry executives
  • Scientists
  • Researchers
  • Educators

Our leadership brings together advanced academic research, executive experience, AI engineering, cybersecurity expertise, and a commitment to developing real-world workforce capability.

  • Portrait of Dr. Beza Lefebo

    Dr. Beza Lefebo

    CEO CAIO

    • AI advisory
    • Technical security engineering
    • Applied AI
    • Responsible AI

    Dr. Beza leads and delivers the cybersecurity engineering and Responsible AI GRC enablement work. He is a hands-on leader who brings years of experience and expertise in advanced cybersecurity engineering, AI governance, risk and compliance, and applied AI solutions. His work sits at the intersection of cybersecurity, AI and business mission. His engagements are transformative: he has led teams of cybersecurity professionals to mature agency cybersecurity, helped businesses establish effective cybersecurity programs, and shared his knowledge across the industry. Dr. Beza has extensive experience in highly regulated industries, including the defense industrial base, the federal government, big tech and the financial sector.

  • Portrait of Dr. John Kuk

    Dr. John Kuk

    Chief Scientist

    • Machine learning
    • AI research
    • Scientific validation
    • System architecture

    Dr. Kuk brings extensive experience in AI research, advanced modeling, enterprise technology transformation, and education. He contributes scientific and technical leadership to the development of AI solutions, research initiatives, and workforce programs, connecting advanced AI concepts with practical organizational needs.

  • Portrait of Dr. John Kramarczyk

    Dr. John Kramarczyk

    Chief AI Advisor

    • AI advisory
    • Technical strategy
    • Cybersecurity analytics
    • Applied research

    Dr. Kramarczyk provides technical and strategic guidance in applied AI, cybersecurity analytics, and emerging technologies. He helps bridge scientific research, technology decisions, and organizational implementation.

  • Portrait of Mr. Rick Roberts

    Mr. Rick Roberts

    VP, Business Development and Delivery

    • Business development
    • Client success
    • Service delivery
    • Defense and federal

    Mr. Roberts brings more than 20 years of technology management experience. A decorated U.S. Marine Corps veteran, he has held senior and technical positions supporting NORAD, the Army and the Pentagon. He takes True CyberChampion's services to clients, makes sure each client's challenge is clearly defined before work begins, and holds the team accountable for delivering what was promised.

Colleagues laugh together while working around a shared table
One team, many disciplines
Two colleagues high-five after a win
We celebrate client wins together
A smiling team meets around a table
Open, respectful debate
Stronger togetherSecurity, AI and people skills in one team

Our culture

Real people, working as one team with yours

Behind every assessment, dashboard and AI system is a team that enjoys hard problems and each other's company. We bring curiosity, candor and care to every engagement, and we measure our success by yours.

  • CollaborationWe work as one team with yours: shared goals, open findings and no surprises.
  • InnovationWe build new tools and methods, from AI prototypes to our own frameworks.
  • AccountabilityNamed owners, quality gates and commitments we keep.
  • Mission firstSecurity and AI serve your mission, not the other way around.

From AI strategy to real-world results

We help organizations establish the rules for AI, build solutions that solve problems, and equip their people with the skills to use AI effectively.

  • AI governance and advisory

    Establish clear policies. Manage risks. Adopt AI with confidence.

    We help organizations develop AI strategies, governance frameworks, responsible-use policies, risk management practices, and oversight mechanisms that support innovation while protecting organizational interests.

    • AI strategy
    • Governance frameworks
    • AI policies
    • Risk assessment
    • Regulatory alignment
    • Executive advisory
    • AI adoption roadmaps
  • AI engineering and applied solutions

    Turn business challenges into working AI solutions.

    Our scientists and engineers design, develop, integrate, and evaluate AI systems for practical organizational applications. We focus on technology that solves defined problems, supports existing workflows, and delivers measurable value.

    • AI solution architecture
    • Machine learning
    • Generative AI
    • AI agents
    • Intelligent automation
    • AI integration
    • Model evaluation
    • Prototyping
    See our engineering work
  • AI skills development and workforce training

    Build the AI skills your workforce needs to perform.

    We design and deliver practical AI training for executives, professionals, technical teams, and entire organizations. Our programs are tailored to organizational policies, approved technologies, job responsibilities, and real workplace challenges.

    • AI literacy
    • Executive education
    • Role-based training
    • Prompt engineering
    • Hands-on labs
    • Workforce assessments
    • AI proficiency development

AI engineering, where building meets proof

Our scientists and engineers design, build, test and field AI systems that solve defined problems. We pair every build with independent evaluation, so you can show what works, how well, and why it is safe to deploy.

From feasibility studies and rapid prototypes to production systems in cloud, hybrid or restricted environments, we bring research rigor and security discipline to every stage.

Research and development: NAICS 541715
BUILD Rapid prototypes LLM and RAG Knowledge graphs Cyber-defense AI Agentic workflows PROVE TEVV benchmarks Red-teaming Bias analysis Robustness tests Explainability FIELDED Secure by design Evidence packs Cloud, hybrid or restricted WHERE BUILDING MEETS PROOF
  • Applied LLM and generative AI systems

    Production LLM applications grounded in your authoritative data, with natural-language interfaces and governed agentic workflows.

    • Retrieval (RAG)
    • Knowledge graphs
    • Chat over data
    • AI agents
  • AI research, development and prototyping

    From feasibility to production: rapid prototypes and R&D roadmaps for problems with no off-the-shelf answer.

    • Feasibility studies
    • Rapid prototypes
    • Novel models
    • R&D roadmaps
  • Test, evaluation, verification and validation

    Independent evidence for deployment decisions: benchmarks, evaluation gates, and adversarial, robustness and bias testing.

    • Benchmarking
    • Red-teaming
    • Bias analysis
    • Explainability
  • NLP and document intelligence

    Turn large document collections into structured, searchable knowledge and faster, more consistent reviews.

    • Semantic similarity
    • Entity extraction
    • Classification
    • Automated review
  • Cyber-defense AI and digital trust

    Models that detect attacks and deception: anomaly detection, deepfakes across voice, image and video, and impersonation fraud.

    • Attack detection
    • Deepfake detection
    • Fraud defense
    • Identity assurance
  • Secure delivery and compliance engineering

    Security-by-design systems with the evidence assessors expect, delivered in cloud, hybrid or restricted environments.

    • Security by design
    • NIST 800-171 / CMMC
    • Evidence architecture
    • Model risk management

Founders who build novel AI models

Our founders developed original AI models in their academic research, each aimed at a real security or trust problem. That research depth shapes how we design and evaluate every system we build.

  • Critical infrastructure attack
    Dr. Beza Lefebo

    Machine learning model to detect cyberattacks on the US smart grid

    Research to protect the systems that keep the power on, by spotting attack activity inside grid operations.

  • Information integrity flagged as fake
    Dr. John Kuk

    AI model to detect fake information online

    Research to identify false and manipulated content as it spreads, so people and organizations can trust what they act on.

  • Healthcare attack detected
    Dr. John Kramarczyk

    Liquid neural network model to detect attacks on medical IoT

    Research using liquid neural networks to recognize attacks on connected medical devices, where safety depends on fast, reliable detection.

  • Proof includedEvery deliverable ships with evaluation evidence: what was measured, how it was measured, and how much results vary.
  • Security-nativeCISSP-led engineering, built with the controls, logging and documentation that regulated environments require.
  • Direct deliveryOur own scientists and engineers do the work: one point of accountability and transparent pricing.

Have a problem with no off-the-shelf answer? Tell us what you need to detect, decide or automate, and we will scope a prototype.

Scope an AI prototype

Customized training

Built on the Capability Proof System™

We do not start with a generic course catalog. Every program follows our methodology: six stages and four integrated frameworks that turn your AI policy into everyday practice, role by role, and prove the change. Explore our full methodology.

Seven failure modes

Why awareness training does not change work

We see seven recurring failure modes. Each one has a known cause in the research, and each one maps to a specific design choice in our system. Select any row to fix it.

0 of 7 fixed
Failure modeWhat it looks likeWhy it failsWhat we do instead
1Generic contentOne deck for everyone, with examples about marketing emails and meal plansSkills transfer when practice resembles the job. Generic examples resemble nobody’s job.Work-TwinTM scenarios built from each role’s real tasks
2Passive formatLecture, video and demo. People watch an expert type prompts.Watching builds familiarity, not skill. Doing beats listening.DRILLTM: people produce first, then critique and improve
3Rules without practiceA slide of do’s and don’ts from the AI policyPeople can recite a rule and still misapply it in a gray-zone casePolicy-to-Practice drills: sort real cases into Go, Sanitize or Stop
4No verification skill“Always check the output,” with no method for checkingAI quality is uneven, and people over-trust it on tasks outside its competenceTrap tasks with planted errors; we measure the catch rate
5Tool tour, not judgmentFeature walkthroughs of one productFeatures change monthly. Judgment about when and how to use AI is what lasts.Tool-agnostic technique plus your approved tools
6One and doneA single session, then nothingUnpracticed skills fade within weeks30/60/90-day micro-drills and launch check-ins
7Measured by satisfactionCompletion rates and smile sheetsHow much people liked a session says little about what they can now doProof FrameworkTM: before-and-after work samples, catch rates, launch ledger

All seven fixed. That is the Capability Proof System: every failure of awareness training answered by a design choice.

Our answer

The Capability Proof SystemTM: six stages, four integrated frameworks

From awareness to evidence. Every engagement moves through six stages in sequence, each ending with a quality check, while four integrated framework components run in parallel underneath. Select a stage to see how it works and which frameworks are at work.

↺ Evidence from each cohort informs the next Stage 1 of 6
Policy, roles, baseline
Outcomes and emphasis
Work-Twins and traps
DRILL labs
Measured before/after
30/60/90 reinforce
Role SignatureTM — who needs what, and where AI can safely help
BELGICTM — what skills, weighted per role
DRILLTM — how skill is built
Proof FrameworkTM — baseline, trap catch rate, launch ledger, Evidence Report
Do · Reflect · Improve · Learn · Launch

Every stage ends in a quality gate that must pass before the next begins, and success is defined up front in a signed Outcome Contract.

Four integrated framework components

FrameworkThe question it answersWhat it produces
Role SignatureTMWho needs what, and where can AI safely help in this role?Role profile, task inventory, Delegation GridTM, Work-TwinTM scenarios
BELGICTMWhich AI capabilities matter most for this role?Weighted capability emphasis per role group; learning objectives
DRILLTMHow does a capability become a habit inside a session?Time-boxed practice cycles; principles written by learners; launched work
Proof FrameworkTMDid it work, for whom, and how do we know?Before-and-after work samples, trap catch rate, Launch Ledger, Evidence Report
Role SignatureTMidentifies what matters
BELGICTMdecides which capabilities to develop
DRILLTMbuilds them through repeated practice
Proof FrameworkTMmeasures what learners can actually do

These four components work together as one integrated training framework. ↺ Continuous improvement: evidence from each training cohort informs the next, allowing us to continuously refine the curriculum, improve delivery and strengthen learning outcomes.

Why our methodology is unique

How our training methodology differs from other AI training

Most AI training on the market falls into three categories. Each has a place. None is built to produce and prove role-specific capability.

DimensionAwareness trainingTool trainingTechnical bootcampsTrue CyberChampion’s Capability Proof SystemTM
Built fromGeneric examplesProduct featuresTechnical curriculumYour roles, tasks and policy
Learner activityWatch and listenFollow alongCodeProduce, critique, improve, launch
CustomizationLogo and examplesNoneBy skill levelRole profile, Delegation GridTM, Work-TwinsTM
Risk and policyA slide of rulesProduct settingsVariesPracticed decisions with trap tasks
AudienceEveryone, the same wayTool usersDevelopersEvery role, differently
Proof of impactCompletion, satisfactionCompletionProjectsBefore-and-after work samples, catch rate, launches
After the sessionNothingHelp articlesAlumni network30/60/90 reinforcement and a 90-day review

Training for every level of your organization

Executive leadership

AI strategy, governance, accountability, enterprise risk, investment decisions, and strategic adoption.

All employees

AI literacy, effective prompting, responsible use, data protection, output verification, and human accountability.

Role-based professional and technical training. Select a group to see how we tailor it.

Role-based training

Finance and investment

Financial analysis, investment research, reporting, forecasting, and verification.

Example exerciseReconcile an AI-generated variance analysis against the source ledgers before it goes to leadership.

Our contributions to AI adoption and skills development

Frameworks and platforms we built and share with the wider industry.

Our commitment: training that changes how people work

Our goal is not simply to teach employees about AI. It is to help them use AI effectively, securely, and confidently within the boundaries established by their organization.

We focus on practical learning, relevant workplace scenarios, and skills that employees can apply immediately.

Bring your AI strategy into everyday work

Whether you need AI governance training, a role-based professional program, or an organization-wide AI proficiency initiative, we can design a program around your policies, people, and priorities.

Discuss customized training
A trainer leads a role-based session while participants applaud
Hands-on labs: people practice with scenarios from their own work

AI governance-to-practice training for your whole workforce

Practical training that turns your AI policy into everyday decisions, delivered in person or virtually. Everyone gets the same foundation, then practices realistic scenarios from their own work in a small, role-based lab.
  1. Diagnose and design

    We map your AI policy to practice, profile each role and its real tasks, and agree measurable outcomes in a one-page Outcome Contract.

  2. Develop

    We build Work-Twin scenarios, trap tasks, Delegation Cards and job aids. Your IT, HR and Legal leads approve every scenario before delivery.

  3. Deliver

    A shared foundation session and role-based DRILL labs, in person, virtually or hybrid. People finish real work with AI under your rules.

  4. Prove and sustain

    Before-and-after work samples, trap catch rates and an Evidence Report for leadership, then 30/60/90-day reinforcement.

Role-based labs

  • Leadership, legal and policyNonpublic information, records, procurement of AI-enabled products, exceptions and escalation
  • Operations and service deliverySensitive customer and partner data, AI-assisted reviews and reports, bias, and checking AI-generated figures
  • Finance, HR and administrationPersonnel and payment data, AI in hiring, and AI-generated payment fraud
  • CommunicationsAccuracy, disclosure, AI images and responding to fake content about your organization
  • Data, research and ITFabricated citations, reproducible analysis, approving tools and handling unapproved AI use
  • Audit and oversightConfidentiality, evidence standards and independence
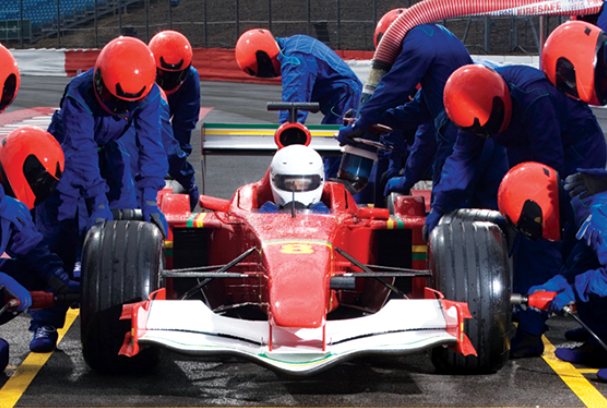
A pit crew services a race car in seconds
Rapid development, high quality

Built fast. Built right.

Custom training usually takes months. We are known for high-quality training solutions developed rapidly. Like a pit crew, our team works in parallel, so your program is ready when you need it, without cutting corners.

  • Parallel buildPolicy mapping, scenario writing and delivery planning happen at the same time
  • Proven frameworksThe Belgic skills framework and the DRILL method give every program a tested structure
  • Quality reviewYour leads review every scenario before it reaches your people
A hybrid training session with people in the room and remote attendees on screen
In person, virtual or hybrid, your choice

Executive and corporate AI talks

Practical talks that build AI literacy, governance capability and strategic execution. Each can run on its own or be tailored to your organization, in person, virtually or hybrid.

Bez0206Building an Enterprise AI Roadmap: From Strategy to ExecutionStrategy and leadership

Learn how to develop a comprehensive AI strategy that aligns with business objectives, identifies high-value use cases, and creates a practical implementation roadmap with clear milestones and success metrics.

What you'll learn

  • How to develop a comprehensive AI strategy aligned with business objectives
  • Methods for identifying and evaluating high-value AI use cases
  • Framework for creating a practical implementation roadmap
  • Techniques for defining clear milestones and success metrics
  • Strategies for securing executive buy-in and resource allocation
  • Approaches for managing organizational change and adoption
OutcomeA clear, actionable AI roadmap tailored to your organization's goals, capabilities, and risk tolerance.
Bez0207Executive AI Governance: Building Trust, Accountability, and OversightGovernance and risk

Establish robust AI governance structures that ensure responsible AI deployment, manage risk, maintain compliance, and build stakeholder trust across your organization.

What you'll learn

  • Core principles of AI governance and responsible AI
  • Framework for establishing AI governance structures
  • Methods for managing AI risk and ensuring compliance
  • Strategies for building stakeholder trust and transparency
  • Approaches for accountability and oversight
  • Best practices for AI policy development
OutcomeRobust AI governance structures that ensure responsible AI deployment, manage risk, and build stakeholder trust.
Bez0208Scaling Generative AI: 10 Best Practices for Enterprise AdoptionStrategy and leadership

Discover proven strategies for scaling generative AI across your enterprise while maintaining security, managing costs, ensuring quality, and maximizing business value.

What you'll learn

  • Proven strategies for scaling generative AI across the enterprise
  • Security and risk management for generative AI
  • Cost management and optimization techniques
  • Quality assurance and output validation
  • Change management and user adoption
  • Measuring and maximizing business value
OutcomeA practical playbook for scaling generative AI while maintaining security, managing costs, and ensuring quality.
Bez0211From Plan to Practice: 5 Steps to Operationalize AI with ConfidenceStrategy and leadership

Move from AI strategy to operational reality with a structured approach that addresses technology integration, workforce enablement, change management, and performance measurement.

What you'll learn

  • Five-step framework for AI operationalization
  • Technology integration strategies
  • Workforce enablement and training approaches
  • Change management best practices
  • Performance measurement and optimization
  • Continuous improvement methodologies
OutcomeA structured approach to move from AI strategy to operational reality with clear steps and success criteria.
Bez0214Functional AI Literacy: What Every Business Unit Needs to KnowWorkforce and functions

Build AI literacy across your organization with practical training tailored to different business functions, enabling informed decision-making and effective AI collaboration.

What you'll learn

  • AI fundamentals for non-technical audiences
  • How AI applies to different business functions
  • Opportunities and limitations of AI
  • Responsible AI use in daily work
  • Collaboration with AI teams and tools
  • Identifying AI opportunities in your area
OutcomeOrganization-wide AI literacy that enables informed decision-making and effective AI collaboration.
Bez0215Use Case Prioritization and Risk Assessment for AI ProjectsGovernance and risk

Learn frameworks for evaluating, prioritizing, and assessing AI use cases based on value, feasibility, risk, and strategic alignment to optimize investment and outcomes.

What you'll learn

  • Frameworks for evaluating AI use cases
  • Value assessment methodologies
  • Feasibility analysis techniques
  • Risk identification and classification
  • Strategic alignment evaluation
  • Prioritization models and tools
OutcomeThe ability to systematically evaluate, prioritize, and assess AI use cases to optimize investment and outcomes.
Bez0217Navigating AI and Algorithmic Liability: Legal and Governance EssentialsGovernance and risk

Understand the legal implications, liability risks, and governance requirements associated with AI deployment to protect your organization and ensure compliance.

What you'll learn

  • Legal implications of AI deployment
  • Algorithmic liability risks and exposure
  • Regulatory requirements and compliance
  • Governance requirements for AI systems
  • Contractual considerations
  • Risk mitigation strategies
OutcomeAn understanding of legal implications, liability risks, and governance requirements to protect your organization.
Bez0221Structuring the AI Organization: Playbook for CDAOsStrategy and leadership

Design effective AI organizational structures, define roles and responsibilities, establish operating models, and build cross-functional collaboration for AI success.

What you'll learn

  • AI organizational design models
  • Role and responsibility definition
  • Operating model development
  • Cross-functional collaboration structures
  • Talent acquisition and development
  • Performance measurement frameworks
OutcomeEffective AI organizational structures with clear roles, operating models, and collaboration mechanisms.
Bez0222Enhancing Customer Service with Generative AIWorkforce and functions

Leverage generative AI to transform customer service operations while maintaining quality, managing risk, and delivering exceptional customer experiences.

What you'll learn

  • Generative AI applications for customer service
  • Implementation strategies and best practices
  • Quality management and oversight
  • Risk management and compliance
  • Customer experience optimization
  • Performance measurement
OutcomeTransformed customer service operations that maintain quality, manage risk, and deliver exceptional experiences.
Bez0223Measuring GenAI ROI: Calculating Business Value and Total CostStrategy and leadership

Develop robust frameworks for measuring generative AI return on investment, calculating total cost of ownership, and demonstrating business value to stakeholders.

What you'll learn

  • ROI frameworks for generative AI
  • Total cost of ownership models
  • Value measurement methodologies
  • Cost allocation strategies
  • Business case development
  • Performance metrics and KPIs
OutcomeRobust frameworks for measuring generative AI ROI, calculating TCO, and demonstrating business value.

Need a course built around your organization's policy, tools and roles? Every program can be customized.

Ask about a talk
Three colleagues review an AI solution together on a tablet
People and AI, working side by side

Artificial intelligence

AI governance, risk, responsible AI and solutions

One AI practice that covers the whole lifecycle: decide how AI is used, find and treat its risks, make it fair and accountable, and put it to work on real problems. Every engagement is role-based, built on your environment and 100% practical.

01 · AI governance

Decide how AI is used, by whom and under what rules

  • AI strategy and enablement roadmaps tied to your mission
  • AI policy, acceptable use and a governance operating model, including AI council and Chief AI Officer support
  • AI use-case intake, approval workflow and inventory
  • Policy to practice: approved tools, data rules, escalation paths and job aids
  • Alignment to the NIST AI RMF, ISO/IEC 42001 and, for federal agencies, OMB M-25-21
NIST AI RMF · ISO/IEC 42001 · OMB M-25-21Discuss AI governance →
02 · AI risk

Find and treat AI risk before it reaches your data, customers or mission

  • Use-case risk tiering and privacy impact review with the GenAI Use Case Assessment Framework (GUAF)
  • AI threat modeling: prompt injection, data leakage, model and agent misuse
  • AI red-teaming, test, evaluation, verification and validation (TEVV)
  • Third-party and vendor AI risk reviews
  • Governance for generative and agentic AI, which banking regulators' 2026 model risk guidance leaves to each institution
NIST AI 600-1 · OWASP Top 10 for LLMs · MITRE ATLASAssess your AI risk →
03 · Responsible AI

Make AI fair, transparent, private and accountable, and prove it

  • Responsible AI principles turned into controls people actually follow
  • Bias and fairness testing, transparency and explainability
  • Human oversight and clear accountability with the Delegation Grid™
  • Algorithmic auditing of AI and automated decision systems
  • Role-based Responsible AI training, from the executive suite to the front line
Trustworthy AI · Proof Pack for your auditorsExplore Trustworthy AI →
04 · AI solutions

Put AI to work on real problems, securely

  • Use-case discovery and return-on-investment measurement
  • Rapid prototypes and production LLM and retrieval (RAG) applications
  • Governed AI agents and workflow automation
  • Microsoft 365 Copilot readiness and rollout
  • Secure deployment in cloud, hybrid and air-gapped environments
Built and tested by our AI engineersSee AI engineering →
A consultant explains an approach to a client team around a conference table
We listen first: your mission, your rules, your risk appetite
Three colleagues study a glowing globe projected from a tablet
Curious, hands-on and always testing what works
Trustworthy AI

Responsible and trustworthy AI, proven in practice: inventory, risk tiers, the Delegation Grid™, assurance testing, and a Proof Pack your auditors can check.

Cybersecurity and information security

Security engineering, compliance and risk, built for what is coming next

We are a cybersecurity engineering and consulting practice. We design and harden cloud environments, build the controls and evidence regulators expect, manage cyber risk at the leadership level, and prepare you for the threats AI and quantum computing are creating.

Two engineers review a tablet in a security operations center
Engineers who build, harden and watch real environments
A security leader presents a resilience strategy to colleagues
Security strategy tied to business resilience

01 · Cybersecurity engineering

Cloud security and secure configuration for Azure and Microsoft 365

Engineers who build, not only advise. We design secure environments, harden them against recognized baselines, and hand over working configurations, code and documentation your team can run.

  • Cloud security architecture

    Secure Azure landing zones on Microsoft’s Cloud Adoption Framework, hub-and-spoke networking, and architecture reviews and threat models for new workloads.

    Landing zonesAzure FirewallPrivate LinkKey Vault
  • Secure configuration and hardening

    Hardened baselines enforced automatically with Azure Policy, drift detection, and a measurable rise in your Defender for Cloud secure score.

    MCSBCISDISA STIGCISA SCuBA
  • Identity and Zero Trust

    Phishing-resistant MFA, Conditional Access, privileged access and access reviews, with a Zero Trust roadmap aligned to CISA’s maturity model.

    Entra IDPIMConditional AccessIntune
  • Microsoft 365 and GCC High security

    Defender XDR and Purview configured end to end, and GCC High or Azure Government environments for CMMC, ITAR and CUI workloads.

    Defender XDRPurview DLPGCC High
  • Security operations engineering

    Microsoft Sentinel deployed with the right data connectors, KQL detections, automated response playbooks and leadership dashboards.

    SentinelKQLLogic AppsM-21-31
  • DevSecOps and infrastructure as code

    Secure Bicep and Terraform modules, policy-as-code checks in the pipeline, and secrets, code and supply-chain scanning.

    BicepTerraformGitHubAzure DevOps
  • Data protection and resilience

    Encryption, data classification, immutable backups and disaster recovery designs that are tested against a ransomware scenario.

    EncryptionAzure BackupDR testing
  • AI and Copilot security

    Microsoft 365 Copilot readiness that fixes oversharing first, and secured Azure OpenAI and AI Foundry workloads with AI threat protection.

    CopilotAzure OpenAIAI Foundry
  • Compliance-driven engineering

    FedRAMP, CMMC, FISMA, HIPAA and PCI DSS requirements turned into real configurations, with evidence pulled from live settings.

    FedRAMPCMMCEvidence automation

Packaged engagements

Defined scope, clear deliverables, predictable price
We build toMicrosoft Cloud Security BenchmarkCIS BenchmarksDISA STIGsCISA SCuBANIST SP 800-53CISA Zero Trust Maturity Model

02 · Compliance

Compliance support for the frameworks you answer to

FISMA, HIPAA, PCI DSS, CMMC and banking regulations ask many of the same questions in different words. We help you build one security program that answers all of them, then produce the evidence each assessor or examiner expects.

One program, five frameworks

Build each control once and map it everywhere. The same risk assessment, policies, access controls and evidence satisfy most of what every framework asks, so you are not paying for five separate compliance projects.

CapabilityFISMANIST SP 800-53 Rev. 5HIPAA45 CFR 164PCI DSSv4.0.1CMMC L2NIST SP 800-171GLBAFTC Safeguards, 16 CFR 314
Risk assessmentRA-3§164.308(a)(1)(ii)(A)12.3.1RA.L2-3.11.1314.4(b)
Policies and security planPL-2§164.31612.1CA.L2-3.12.4314.3(a)
Access control and MFAAC-2, IA-2§164.312(a)(1), (d)8.4.2IA.L2-3.5.3314.4(c)(1), (c)(5)
EncryptionSC-13, SC-28§164.312(a)(2)(iv), (e)(2)(ii)3.5.1, 4.2.1SC.L2-3.13.11314.4(c)(3)
Logging and monitoringAU-2, AU-6, SI-4§164.312(b)10.2.1AU.L2-3.3.1314.4(c)(8)
Incident responseIR-4, IR-8§164.308(a)(6)12.10.1IR.L2-3.6.1314.4(h)
Vendor and third-party riskSA-9, SR-6§164.308(b)12.8ESP scoping, 32 CFR 170.19314.4(f)
Security awareness trainingAT-2§164.308(a)(5)12.6AT.L2-3.2.1314.4(e)
Ongoing assessmentCA-7§164.308(a)(8)11.3CA.L2-3.12.3314.4(d)

Representative references, not a complete mapping. Banks follow the parallel Interagency Guidelines under GLBA. We produce the full crosswalk for your environment as part of an engagement.

  1. Assess

    Scope the systems and data in play, then run a gap or readiness assessment against the framework that applies.

  2. Build

    Write the policies, procedures and system security plan, implement or tune controls, and open a realistic POA&M.

  3. Prove

    Organize evidence the way your assessor will test it, run a mock assessment, and support you through the real one.

  4. Sustain

    Continuous monitoring, ISSO and virtual CISO support, annual reviews and security awareness training for your staff.

AI is now in scope for every framework

Your staff already use AI tools with regulated data. We extend each program to cover AI tools, models and data flows, mapped to the NIST AI Risk Management Framework, so your next assessment does not find a gap you never planned for.

Request a readiness assessment

Recent work: FISMA assessment and authorization support for financial-services platforms, an RMF authorization package for a cleared contractor's classified system, CMMC Level 2 readiness for defense manufacturers, and FedRAMP 20x control mapping.

03 · Continuous monitoring and reporting

See your security posture every day, not once a year

We connect your tools, track every control continuously, and turn the results into dashboards and reports your leaders, auditors and examiners can use. Try the demo below: switch frameworks, hover the charts and generate an executive report.

Security posture · Sample organizationSample data for demonstrationLIVE DEMO

Control implementation over time

Implementation by control area

Percent of controls fully implemented. Hover a row for detail.

    Implemented90% target⚠ Below 80%

    Live findings feed

      Illustrative demo with simulated data. In an engagement, the same views are built on your own Microsoft Sentinel, Defender for Cloud, Purview and ticketing data.

      • Continuous control monitoringControls checked against live settings, with drift flagged the day it happens.
      • Automated evidenceEvidence collected from your systems on a schedule, ready for assessors and examiners.
      • Executive and board reportingMonthly posture reports, risk trends and plain-language summaries for leadership.
      • FISMA and FedRAMP ConMonMonthly scan results, POA&M updates and continuous monitoring deliverables.

      Want dashboards like this on your own data? We set up monitoring and reporting in weeks, not months.

      Set up continuous monitoring

      04 · Cyber risk

      Cyber risk your leadership can see, decide on and defend

      Security budgets follow risk. We assess it, put it in business terms, and give your executives and board a clear picture of what matters most and what it will take to fix.

      1. Cybersecurity risk assessment and risk registerThreats, vulnerabilities and impacts assessed with NIST SP 800-30, recorded in a register your leaders can act on.
      2. Program maturity assessment and roadmapWhere you stand against NIST CSF 2.0 today, where you need to be, and a prioritized plan to get there.
      3. Virtual CISO and ISSO supportExperienced security leadership on demand, including board and executive reporting.
      4. Third-party and supply-chain riskVendor tiering, security questionnaires, contract terms and ongoing monitoring of the providers you depend on.
      5. Business impact analysis and resilienceCritical processes, recovery objectives, continuity and disaster recovery plans that are actually tested.
      6. Incident response planning and tabletop exercisesPlans built around your notification deadlines, rehearsed with your executives before a real incident.
      7. Policy and standards programA complete, right-sized policy set mapped to the frameworks you answer to, with a review cycle that keeps it current.

      05 · Emerging threats

      Ready for the threats arriving now

      AI has lowered the cost of attack, and the next wave will not look like the last one. We track what is changing and turn it into specific controls, training and plans for your organization.

      • Rising

        AI-powered phishing and deepfake fraud

        Cloned voices and video of executives now approve fake payments and reset passwords, and AI writes phishing that has no typos.

        How we helpVerification protocols for payments and help-desk resets, deepfake awareness training, and detection support.
      • Rising

        Attacks on your own AI

        Prompt injection, data leakage through AI assistants, and AI agents tricked into taking actions they should not.

        How we helpAI threat modeling, guardrails, least-privilege agent design and AI red-teaming against OWASP and MITRE ATLAS.
      • Rising

        Identity and session attacks

        MFA fatigue, stolen session tokens and malicious app consent let attackers walk past passwords and basic MFA.

        How we helpPhishing-resistant MFA, Conditional Access, token protection and identity threat detection.
      • Rising

        Ransomware and extortion

        Attackers now steal data before encrypting it, and target backups first so recovery fails.

        How we helpImmutable backups, segmented recovery, tested restore times and executive tabletop exercises.
      • Rising

        Cloud and SaaS supply chain

        One compromised vendor, integration or misconfigured cloud service can expose every customer at once.

        How we helpPosture management, SaaS app governance and third-party risk reviews of your critical providers.
      • Rising

        Quantum risk to encryption

        NIST has published post-quantum encryption standards, and data stolen today can be decrypted later.

        How we helpA cryptographic inventory and a migration roadmap to post-quantum algorithms (FIPS 203, 204 and 205).
      An executive team meets around a boardroom table

      Not sure which of these matter most to you? A short threat briefing for your leadership team is a good place to start.

      Request a threat briefing

      How we work

      One disciplined way of working, across every practice

      Every engagement follows a documented workflow with defined steps, deliverables and quality gates, aligned to the standards our clients answer to.

      Explore how we work, step by step →

      • Quality gatesEvery stage ends in a check that must pass
      • Evidence over assertionWe show what was measured and tested
      • Standards-alignedMapped to NIST, ISO and federal frameworks
      • Two-person reviewA second qualified reviewer on every deliverable
      • Plain languageDecisions, not jargon
      Seen from above, a group works around a table on a training plan
      Learn, practice, apply: built for how adults learn

      Why True CyberChampion

      We combine deep technical expertise with executive-level strategic guidance to deliver practical, assessment-ready outcomes.

      Clarity over complexity

      We turn complex cybersecurity, compliance, and AI governance requirements into clear, manageable actions your team can understand and execute with confidence.

      A predictable delivery framework

      We deliver every engagement through frameworks we built: the Belgic AI skills framework, the DRILL method for teaching AI skills to adults, and the iCRAFT Prompts online learning platform. We are scientists, and dedicated educators.

      Federal contract experience

      We bring current experience supporting federal government environments and understand the operational, compliance, and documentation expectations required.

      Tailored, not templated

      Our deliverables are built around your organization, workflows, technology environment, and security posture so the end result is relevant, usable, and credible.

      Personalized client care

      We provide responsive, hands-on support and work closely with your team throughout the engagement to ensure progress, alignment, and practical results.

      Deep AI expertise

      We are scientists, researchers and educators who design and build solutions to real problems. Our team brings AI governance, risk, and compliance experience across a wide range of environments.

      Ready to strengthen your cybersecurity and AI governance?

      Schedule a consultation to discuss your organization's challenges and how we can help you achieve compliance, manage risk, and scale AI with confidence.

      Frequently asked questions

      Answers to common questions about our services, approach, and engagement process.

      What types of organizations do you work with?

      We serve a diverse range of clients including:

      • Federal agencies at all levels
      • Defense contractors and the Defense Industrial Base
      • Big tech companies and technology firms
      • Private sector organizations across industries
      • Regulated industries (healthcare, finance, critical infrastructure)
      • Small and mid-sized businesses

      Our expertise spans both public and private sector environments with particular strength in federal compliance frameworks and emerging AI governance requirements.

      How is your approach different from other cybersecurity consultants?

      Several key differentiators set us apart:

      • Evidence-first execution: We focus on practical, assessment-ready outputs rather than theoretical frameworks
      • Tailored solutions: We customize every engagement to your specific environment rather than using templated solutions
      • Hands-on partnership: We provide responsive, personalized support throughout the engagement
      • Federal experience: We bring current experience supporting federal government environments
      • Executive-level advisory: We work directly with leadership teams to ensure strategic alignment
      What is your experience with federal compliance requirements?

      We have current, hands-on experience supporting federal government environments with deep expertise in:

      • FISMA compliance and continuous monitoring
      • Risk Management Framework (RMF) implementation
      • CMMC requirements for defense contractors
      • Federal information security policies and standards
      • NIST frameworks and guidelines
      • Audit preparation and response

      We understand the operational, compliance, and documentation expectations required to serve regulated and mission-driven organizations effectively.

      Do you support HIPAA and PCI DSS as well as federal frameworks?

      Yes. Alongside FISMA and CMMC, we support HIPAA Security Rule risk analysis and safeguards for healthcare organizations and their business associates, and PCI DSS v4.0.1 scoping, gap assessment and remediation for merchants and service providers. Because the frameworks overlap, we build one control set and map it to each.

      We are not a C3PAO or a PCI Qualified Security Assessor (QSA). We prepare you for those assessments and stay independent of them. See compliance support.

      Do you provide training for our executive team and staff?

      Yes, executive training is a core part of our service offerings. We provide comprehensive training programs including:

      • Executive AI training: Programs on AI governance, strategy, risk management, and responsible AI deployment
      • Corporate training: Functional AI literacy, use case assessment, compliance awareness, and cybersecurity best practices
      • Custom programs: Tailored training designed for your organization's specific needs, industry, and maturity level

      All training is practical, interactive, and designed for real-world application. Available in-person, virtual, or hybrid formats.

      How do you engage with clients and what does the process look like?

      Our typical engagement process includes:

      • Initial consultation (free): Discussion of your challenges and objectives
      • Discovery and assessment: Deep dive into current state and requirements
      • Proposal development: Tailored scope, deliverables, and timeline
      • Engagement execution: Collaborative work with regular progress updates
      • Delivery and transition: Final deliverables, knowledge transfer, and post-engagement support

      We work closely with your team throughout, ensuring alignment and practical results.

      What makes you qualified to advise on AI governance and risk?

      Our team brings deep expertise in both cybersecurity compliance and emerging AI governance frameworks including NIST AI RMF. We combine technical knowledge with strategic advisory capabilities to help organizations navigate the complex intersection of AI innovation, risk management, and regulatory compliance. Our approach is grounded in practical experience and evidence-based methodologies.

      What is the typical timeline for a compliance or AI governance engagement?

      Engagement duration varies by scope:

      • Assessment projects: 2 to 6 weeks
      • Compliance readiness: 3 to 9 months
      • RMF authorization support: 6 to 18 months
      • AI governance program development: 3 to 6 months
      • Training programs: 1 day to several weeks
      • Advisory retainers: Ongoing (monthly or quarterly)

      We work with you to establish realistic timelines based on your needs and constraints.

      How do you ensure confidentiality and security of our information?

      We treat all client information with the highest level of confidentiality:

      • Non-disclosure agreements (NDAs) executed before engagements
      • Secure handling and storage of all client data
      • Restricted access on a need-to-know basis
      • Secure communication channels
      • Proper disposal of sensitive materials
      • Compliance with client security requirements

      Your trust is fundamental to our work.

      Let's plan your training

      Tell us about your team, your AI policy and your timeline. We typically respond within one business day.

      Email
      info@truecyberchampion.com
      beza@truecyberchampion.com (federal government point of contact)
      Phone
      Main: +1 (202) 799-4272
      Federal government: 240-476-3268
      Address
      11393 Columbia Pike #D10
      Silver Spring, MD 20904
      Washington, DC metro area
      Business information
      CAGE code: 9DE87
      UEI: UEQDZSKKRFGC65
      NAICS: 611430, 611420, 541611, 541690, 541715, 541511, 541512, 541519, 518210
      Business hours
      Monday to Friday, 9:00 AM to 6:00 PM Eastern

      We use your details only to respond to this request.

      ↑ ↓ to moveEnter to openEsc to close